Hackers Don't Work on an Annual Schedule. Neither Should Your Security.

 Move beyond outdated security tests. Continuously detect, prioritize, and fix vulnerabilities across your entire attack surface in real time.

From shadow IT to zero-day threats—we find risks the moment they appear.

Your Security Is Already Outdated.

Security gaps appear daily. Annual testing can’t keep up.

Annual Pentest Completed

January 2024

New Server Deployed

February 2024

Vulnerability Stays Hidden

For months…

Exposure Window: 11 months until next test

Continuous Security That Never Sleeps

Real-time vulnerability detection and risk management that operates 24/7/365

Asset Added

New server, cloud instance, or
device joins your network

Instantly Scanned

Automated vulnerability
assessment begins immediately

Risk Prioritized

RBVM engine ranks threats by
actual business impact

Patch Recommended

Actionable remediation steps
delivered to your team

Core VAM Capabilities

Comprehensive attack surface management and vulnerability detection

Dynamic Asset Discovery

Automatically identify and catalog all IT assets across cloud, on-premise, and hybrid environments in real-time.

Continuous Vulnerability Scanning

24/7 automated scanning detects vulnerabilities, misconfigurations, and security weaknesses the moment they appear.

Attack Surface Mapping

Visualize your entire digital footprint including shadow IT, forgotten assets, and external-facing systems.

Risk-Based Prioritization (RBVM)

Intelligent risk scoring considers exploitability, asset criticality, and threat intelligence to focus on what matters.

Zero-Day Exposure Detection

Instant identification when new CVEs are published, with immediate assessment of your exposure across all assets.

Cloud & Network Misconfiguration Detection

Identify exposed S3 buckets, open ports, weak authentication, and configuration drift before attackers do.

You Can't Secure What You Can't See

Comprehensive visibility across your entire attack surface

Servers

247

Monitored

APIs

247

Monitored

Cloud Assets

412

Resources

Unknown Devices

23

Shadow IT

Hidden Assets = Hidden Risks

On average, organizations have 30% more assets than they realize. Each unknown asset is a potential entry point for attackers.

Shadow IT Discovery

Detect unauthorized cloud services, forgotten test servers, and rogue devices before they become breach vectors.

Complete Asset Inventory

Maintain an always-current inventory of every server, application, cloud resource, and endpoint in your environment.

How Continuous VAM Works

Six-step process for continuous vulnerability management

Discover All Assets

Automated asset discovery across
internal networks, cloud environments,
and external-facing systems.
Internal + External + Cloud

Continuously Scan for Vulnerabilities

24/7 automated scanning detects CVEs,
misconfigurations, and security
weaknesses.
Always-On Detection

Identify Real Threats

RBVM engine filters out noise and
identifies vulnerabilities with actual
exploit potential.
Risk-Based Validation

Prioritize Critical Risks

Intelligent scoring ranks vulnerabilities by
business impact, exploitability, and asset
value.
Focus on What Matters

Alert with Actionable Fixes

Receive clear remediation guidance with
specific patches, configuration changes,
and timelines.
No Alert Fatigue

Track & Verify Remediation

Automated validation confirms
vulnerabilities are properly patched and
risks are eliminated.
Closed-Loop Process

We Don't Give Reports. We Give Action.

The DefendX advantage: actionable intelligence without the noise

No Alert Fatigue

Intelligent filtering eliminates false positives and low-priority findings. Only critical, actionable alerts reach your team.

Real-Time Security Posture

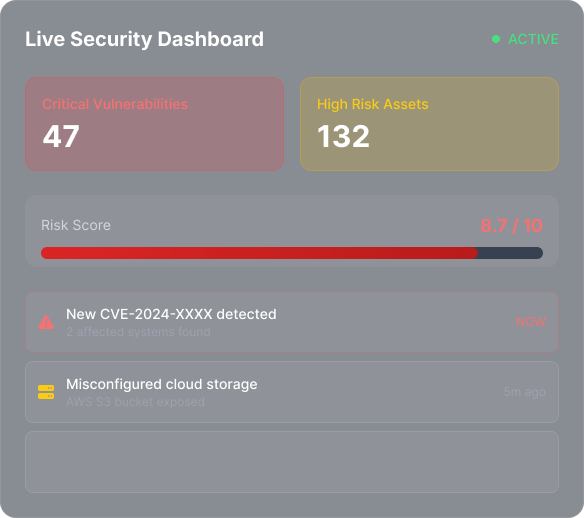
Live dashboard shows your current risk score, trending vulnerabilities, and remediation progress at a glance.

Integrated Patch Management

Seamless workflows connect vulnerability detection directly to patch deployment and verification systems.

Continuous Compliance

Automated evidence collection and reporting for ISO 27001, SOC 2, PCI DSS, and other regulatory frameworks.

When a New Threat Drops, You're Already Covered

Instant zero-day response and exposure assessment

New CVE Published

Critical vulnerability announced in widely-
used software component

Breaking News Alert

Instant System Scan

Automated assessment checks all assets
for exposure to the new vulnerability

Scanning in Progress...

Instant System Scan

Automated assessment checks all assets
for exposure to the new vulnerability

Scanning in Progress...

Average Time to Detection

Average exposure window

180 days

Average exposure window

Average exposure window

< 5 minutes

From CVE publish to alert

Real Use Cases

How continuous VAM prevents real-world security incidents

Misconfigured Cloud Storage Detected Instantly

Developer creates new S3 bucket with public read
permissions during testing. DefendX flags the exposure
within 5 minutes, preventing potential data leak.

CEO Impersonation Attempt Blocked

Fraudulent domain registered mimicking CEO email.
DefendX alerts security team before wire transfer scam
email is sent.

Zero-Day Vulnerability Identified Early

New Log4Shell-style vulnerability announced. DefendX
scans entire infrastructure, identifies 47 affected systems,
and provides patch guidance within 10 minutes.

Critical Patch Applied Before Exploit

High-severity vulnerability detected in production web
server. Integrated workflow triggers patch deployment,
verification scan confirms successful remediation.

Stop Waiting for the Next Security Test.

Continuously detect. Prioritize. Fix. Stay secure every single day.
Zero-Day Detection Time
< 0 min
Continuous Monitoring
0 /7
Attack Surface Visibility
0 %