Advanced SIEM & SOAR-powered SOC that detects, analyzes, and responds to cyber threats in real time—before they become breaches.
Hackers don’t sleep. Neither do we.
Thousands of alerts every day. Real threats get buried in the noise.
2,847 events/hour
1,234 alerts/day
5,692 entries/hour
Thousands
Without correlation and analysis, critical alerts go unnoticed until it's too late
Collect and centralize logs from allsystems, applications, and networkdevices
SIEM analyzes patterns andidentifies genuine security threatsinstantly
Advanced algorithms identifyattacks, anomalies, and suspiciousbehavior
SOAR executes instantcontainment actions withouthuman intervention
Enterprise-grade SIEM platforms(Splunk/Wazuh) with custom correlationrules, threat intelligence feeds, and real-time dashboards.
Unified log collection from firewalls,endpoints, servers, cloud platforms, andapplications with long-term retention.
Pre-configured playbooks automaticallyisolate threats, block IPs, disableaccounts, and contain incidents withinseconds.
Expert security analysts actively searchfor hidden threats, APTs, and attackerbehavior before alerts trigger.
Machine learning models establishbaselines and detect deviationsindicating insider threats or compromisedaccounts.
Intelligent correlation engine connectsdisparate events to identify multi-stageattacks and eliminate false positives.
No human intervention required. Automated playbooks respond faster than any attacker.
Aggregate security logs from firewalls,endpoints, servers, cloud platforms,applications, and network devices.Complete visibility across infrastructure
SIEM normalizes diverse log formats andcorrelates events across systems toidentify patterns and relationships.Transform noise into intelligence
Advanced analytics and threatintelligence identify suspicious behavior,attacks, and security violations.Real-time threat identification
SOAR executes pre-configured responseworkflows: block IPs, isolate devices,disable accounts, quarantine files.Instant automated containment
Expert security analysts review high-priority incidents, conduct forensicanalysis, and validate automatedresponses.Human expertise + automation
Complete incident documentation, rootcause analysis, remediation verification,and executive reporting.Full transparency & compliance
Dedicated security analysts actively monitor your environment around the clock, every day of the year.
Intelligent correlation eliminates 95% of false positives. You only see real threats that require action.
SOAR playbooks instantly isolate threats, block attacks, and contain incidents before damage occurs.
Get Fortune 500-level security operations at a fraction of the cost of building your own SOC team.
Advanced Persistent Threats hide for months. Our analysts hunt for indicators of compromise, unusual patterns, and attacker tradecraft.
Detect attackers moving between systems, escalating privileges, and exploring your network before they reach critical assets.
Identify stealthy techniques like living- off-the-land attacks, credential abuse, and data exfiltration attempts.
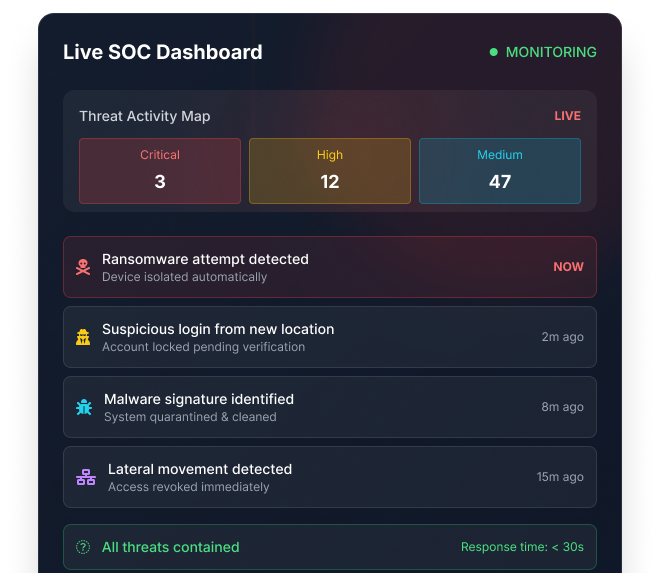
SIEM identifies login from new country at unusual time.SOAR automatically locks account and requires MFAverification.
Endpoint detects malware signature. SOAR instantlyisolates infected device from network and initiates remotecleanup.
Behavioral analytics detect employee downloading unusualvolumes of sensitive data. Immediate investigation andaccess restriction.
Mass file encryption detected. SOAR kills maliciousprocesses, isolates system, and restores from cleanbackup automatically.
Get 24/7 monitoring, real-time detection, and instant response—without buildingyour own SOC.