We Turn Compliance into Your Competitive
Advantage
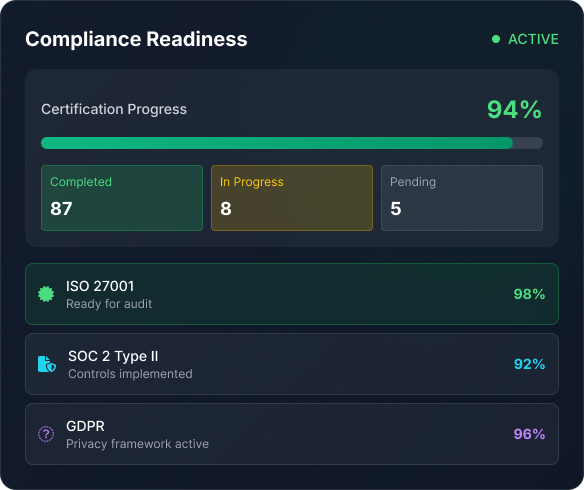
DefendX provides end-to-end Governance, Risk & Compliance (GRC) advisory to
help you get certified faster, pass audits confidently, and unlock enterprise
deals.
Get Certified Faster
Streamlined certification process with expert guidance reduces time-to- certification by 60%. No more guesswork or delays.
Pass Audits Confidently
Comprehensive audit preparation with evidence collection, mock audits, and auditor support ensures first-time certification success.
Unlock Enterprise Deals
Compliance certifications open doors to Fortune 500 clients and high-value contracts previously out of reach.
We Don't Just Consult — We Build,
Implement, and Support Your Entire
Compliance Journey
Gap Analysis & Risk Assessment
Identify exactly what's missing and prioritize remediation efforts
Policy & Documentation Creation
Complete ISMS documentation tailored to your business operations
Technical Control Implementation
Deploy security tools, access controls, and monitoring systems
Team Training & Awareness
Prepare your team for audits with comprehensive training programs
Audit Support & Defense
We sit with you during audits to answer questions and defend
implementation
End-to-End Support
Assessment
Implementation
Certification
Maintenance
Our GRC Capabilities
Comprehensive governance, risk, and compliance services for every certification
need
We're not just consultants—we're your compliance partners
Business-Aligned Security
We design compliance frameworks that support your growth—not slow it down. Every control is practical, implementable, and aligned with your business objectives.
Fractional CISO Support
Get expert leadership without hiring a full-time executive. Our fractional CISOs provide strategic guidance, board reporting, and executive-level security leadership.
Audit-Ready Execution
We don’t just advise—we sit with you during audits. Our team helps answer auditor questions, defend your implementation, and ensure certification success.
Automated Compliance
Reduce manual work with automated evidence collection. Our technology platform continuously monitors compliance status and maintains audit-ready documentation.
Turn Compliance into Revenue
Without certifications, enterprise clients won't trust you. With DefendX,
compliance becomes your sales enabler, not a blocker.
Close High-Value Deals
Faster
Skip security review delays and close
enterprise contracts 3x faster with ready
compliance certifications.
Average deal acceleration: 60 days
Pass Vendor Security
Checks
Answer security questionnaires with
confidence. Certifications prove your
security posture to procurement teams.
Questionnaire completion: 80%
faster
Build Trust with Global
Clients
International certifications signal maturity
and reliability, opening doors to Fortune
500 and global enterprises.
Enterprise win rate: +45%
Compliance Becomes Your Sales Enabler, Not a Blocker
Transform compliance from a cost center into a revenue driver. Win bigger deals, enter new markets, and differentiate
from competitors.
3x
Faster deal closures
$2M+
Average contract value increase
95%
First-time certification success
Trusted Certifications We Support
Global compliance standards and frameworks
ISO 27001
SOC 2
GDPR
HIPAA
DPDP Act
Frequently Asked Questions
Everything you need to know about GRC compliance
How long does ISO 27001 certification take?
With DefendX, most organizations achieve ISO 27001 certification in 4-6 months. Timeline depends on your current security posture, organization size, and commitment level. We provide a detailed roadmap during the initial assessment.
What is the cost of compliance certification?
Costs vary based on organization size, scope, and certification type. Investment typically ranges from $25K-$100K for complete implementation and certification. This includes gap assessment, implementation, documentation, and audit support. ROI is achieved through enterprise deal closures and risk reduction.
Do we need internal team support?
Yes, but minimal. We handle the heavy lifting—documentation, policy creation, and implementation. Your team provides business context, approves policies, and participates in training. Typical commitment: 5-10 hours per week from key stakeholders.
What happens after certification?
Certifications require annual surveillance audits and recertification every 3 years. We provide ongoing support for continuous compliance, annual audits, and recertification. Our automated platform maintains audit-ready documentation year-round.
Can you help with multiple certifications simultaneously?
Absolutely. Many controls overlap between ISO 27001, SOC 2, GDPR, and HIPAA. We design integrated frameworks that satisfy multiple standards efficiently, reducing duplication and accelerating time-to certification.
Ready to Get Certified and Close Bigger
Deals?
Start your compliance journey today with a free gap assessment
Request Security Consultation
What You'll Get
Free Compliance Gap Assessment
Detailed analysis of your current state vs. certification
requirements
Customized Roadmap
Step-by-step plan with timeline and resource requirements
Expert Consultation
30-minute call with a GRC expert to discuss your specific
needs
Cost Estimate
Transparent pricing for complete certification journey