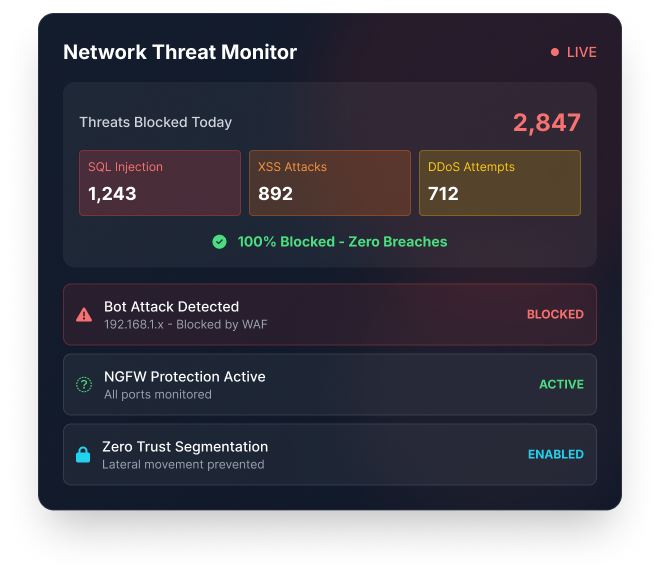
DefendX designs and manages advanced network security architectures using
Next-Generation Firewalls (NGFW), Web Application Firewalls (WAF), and Zero
Trust segmentation.
Next-Gen Firewalls
(NGFW)
Advanced threat prevention with deep packet inspection, intrusion prevention, and intelligent traffic filtering.
Web Application Firewalls
(WAF)
Layer 7 protection blocking SQL injection, XSS, and API attacks before they reach your applications.
Zero Trust Segmentation
Micro-segmentation architecture preventing lateral movement and isolating critical assets.
We don't just install security — we continuously monitor, optimize, and
defend your infrastructure.
Active threat hunting + real-time rule optimization + 24/7 monitoring = Network security that evolves with threats
Continuous Monitoring
24/7 threat detection and
response
Rule Optimization
Weekly firewall policy reviews
Threat Intelligence
Real-time attack signature
updates
Expert Support
Dedicated security engineers
Our Network Security Expertise
Comprehensive network defense capabilities for modern infrastructure
Next-Gen Firewall (NGFW) Hardening
Advanced perimeter protection with intelligent threat
prevention
Deep Packet Inspection (DPI) - Analyze traffic at application layer for hidden threats
Intrusion Prevention Systems (IPS) - Real-time blocking of known attack patterns
Advanced Access Control (ACLs) - Granular rule sets based on identity and context
Controlled access to internal systems - Role-based VPN policies
Split-tunnel optimization - Balance security and performance
How We Secure Your Network
Our proven methodology ensures comprehensive network protection from day
one
Audit
Analyze current firewall & traffic logs
Rule review
Traffic analysis
Vulnerability scan
Harden
Remove weak rules & configure advanced security
Rule cleanup
ACL optimization
IPS tuning
Deploy
Implement NGFW & WAF layers
NGFW setup
WAF deployment
Segmentation
Optimize
Tune rules to avoid false positives
Baseline creation
Policy refinement
Performance tuning
Monitor
Continuous threat detection & updates
24/7 monitoring
Threat hunting
Weekly reviews
Why DefendX Stands Out
Network security that adapts to your business, not the other way around
No "Set & Forget" Security
We continuously tune your firewall rules based on real- time threats. Weekly policy reviews ensure your defenses evolve with attack techniques, not lag behind them.
Zero Business Disruption
High-availability architecture ensures no downtime during updates. Redundant failover systems and change windows aligned with your business hours keep operations running smoothly.
Precision WAF Tuning
We block attackers — not your real customers. Custom rule sets eliminate false positives while maintaining aggressive threat protection. Your users experience seamless access.
Compliance-Ready Security
Aligned with PCI-DSS, ISO 27001, and SOC 2 requirements. Our firewall configurations include audit logging, change management, and evidence collection for certification readiness.
Block Attacks Before They Reach You
Every day your systems face relentless attacks — DefendX stops them at the
edge
Every day your systems face:
Bot Attacks
Automated scraping and credential stuffing attempts
Credential Stuffing
Stolen password lists tested against your login endpoints
Data Scraping
Unauthorized extraction of proprietary information
DDoS Attempts
Volumetric and application-layer denial of service
With DefendX:
Malicious traffic is stopped at the edge
WAF and NGFW filter attacks before they consume server
resources or expose vulnerabilities.
Your servers stay protected
Application and database layers never see malicious
requests, reducing attack surface dramatically.
Your business stays online
DDoS mitigation and high-availability architecture ensure
continuous service even under attack.
We filter the bad — and let your customers in seamlessly.
Precision threat detection means legitimate users experience zero friction while attackers hit an impenetrable wall.
99.9%
Attack blocking rate
<0.01%
False positive rate
0ms
Added latency for users
Network Security Architecture
Multi-layered defense protecting every entry point
Before DefendX
Internet
Direct exposure to threats
Basic Firewall
Unclear which ones apply to you
Application Servers
Vulnerable to attacks
High Risk of Breach
After DefendX
Internet
Public traffic entry point
WAF Layer
OWASP Top 10 protection
NGFW + IPS
Deep packet inspection
Zero Trust Zones
Micro-segmented workloads
Maximum Security Posture
Frequently Asked Questions
Everything you need to know about network security and WAF
Do I need both NGFW & WAF?
Yes, for comprehensive protection. NGFW protects your network perimeter (Layer 3-4), while WAF defends web applications (Layer 7). NGFW blocks network-level attacks like port scans and malware, while WAF stops application attacks like SQL injection and XSS. Together, they provide defense-in-depth.
Will this slow down my website?
No. Modern WAFs add less than 1ms latency, imperceptible to users. Our optimization ensures security rules process efficiently without impacting performance. In fact, by blocking malicious traffic, we often improve response times by reducing server load.
How fast can implementation happen?
Initial deployment: 2-4 weeks. Basic NGFW and WAF protection can be live within 48-72 hours for urgent needs. Full optimization including Zero Trust segmentation takes 3-6 weeks depending on network complexity. We provide phased rollout to minimize business disruption.
What if I already have a firewall?
We audit and optimize existing infrastructure first. If your current firewall is modern enough, we’ll harden it rather than replace it. For legacy systems, we recommend upgrades to NGFW capabilities. Our goal is cost-effective security, not unnecessary hardware sales.
Do you support cloud environments?
Absolutely. We deploy cloud-native WAF solutions for AWS, Azure, and GCP, along with virtual NGFW appliances. Hybrid and multi-cloud architectures are supported with unified policy management across all environments.
Ready to Get Certified and Close Bigger
Deals?
Start your compliance journey today with a free gap assessment
Request Security Consultation
What You'll Get
Free Compliance Gap Assessment
Detailed analysis of your current state vs. certification
requirements
Customized Roadmap
Step-by-step plan with timeline and resource requirements
Expert Consultation
30-minute call with a GRC expert to discuss your specific
needs
Cost Estimate
Transparent pricing for complete certification journey