Under Attack? We Stop the Breach — Fast.
Immediate incident response, threat containment, and
forensic analysis to minimize damage and get your business
back online.
Every minute = potential data loss, system damage, and business
disruption
A Security Breach Isn't Just Technical — It's Business Critical
Every second counts when your organization is under attack

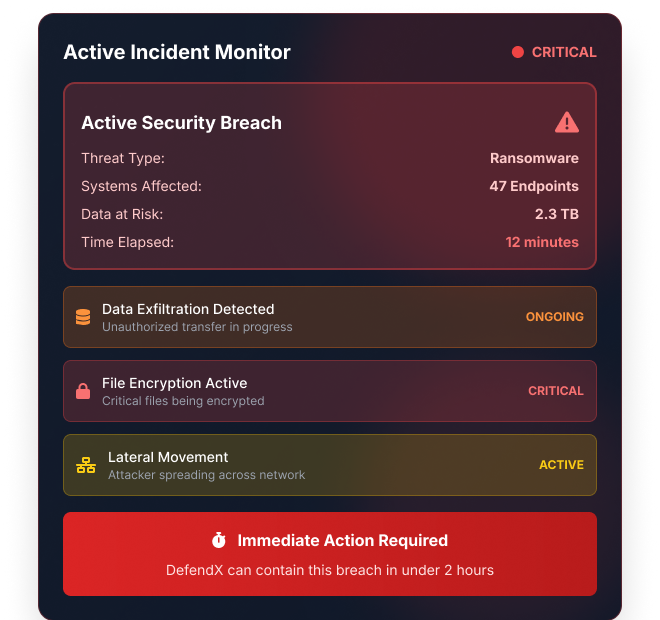
Ransomware locking your systems
Critical business operations halted. Files encrypted. Ransom
demands increasing by the hour. Your team is paralyzed, unable to access essential data.
- Average downtime: 21 days without expert response

Hackers stealing sensitive data
Customer records, financial data, intellectual property being
exfiltrated in real-time. Compliance violations mounting. Legal
liability growing exponentially.
- Data breach costs average $4.45M per incident

Websites or apps going down
Revenue streams disrupted. Customers unable to access services.
Brand reputation damaged with every passing minute. SLA breaches
accumulating.
- $5,600 lost per minute of downtime (average)

Panic decisions causing more damage
Shutting down systems incorrectly. Destroying forensic evidence.
Making wrong containment decisions. Turning a recoverable incident
into a catastrophe.
- 65% of breaches worsen due to improper response
Reality: One wrong move can destroy evidence and increase losses
Without structured incident response, panic leads to irreversible mistakes. Evidence gets destroyed. Attackers remain hidden. Recovery becomes impossible.
We Act Like Your Cybersecurity First Responders
DefendX provides rapid, structured Incident Response (IR) to protect your business when every second matters
Contain the attack immediately
Isolate compromised systems, block malicious traffic, and stop lateral movement within minutes
Remove attackers completely
Eliminate malware, backdoors, and persistence mechanisms to ensure threats are fully eradicated
Investigate how it happened
Forensic analysis to trace attack vectors, identify vulnerabilities, and preserve evidence
Secure your systems for the future
Implement hardening measures and controls to prevent recurrence and strengthen defenses
We don't just fix — we take control of the situation
Our certified incident response team brings calm, structure, and expertise to chaos. We guide your leadership through every decision, preserve critical evidence, and restore operations safely.
<15 min
Initial response time
<2 hrs
Threat containment
100%
Evidence preservation
Our Network Security Expertise
Comprehensive network defense capabilities for modern infrastructure
Immediate Threat Containment
Stop the attack from spreading and minimize damage
- Isolate infected systems - Quarantine compromised endpoints and servers
- Block malicious traffic - Implement emergency firewall rules and ACLs
- Disable compromised accounts - Revoke credentials and enforce password resets
- Stop lateral movement instantly - Segment network to prevent attacker pivoting
Digital Forensics & Traffic Analysis
Understand the attack to prevent recurrence
- Identify attack entry point - Trace initial compromise vector
- Analyze logs & network activity - Deep dive into system and traffic logs
- Detect data exfiltration - Identify what data was accessed or stolen
- Trace attacker behavior - Map the kill chain and tactics used
Eradication & System Recovery
Remove all threats and restore clean operations
- Remove malware & backdoors - Complete threat elimination from all systems
- Patch exploited vulnerabilities - Close security gaps that enabled the breach
- Secure system configurations - Harden settings to prevent reinfection
- Restore clean operations - Safely bring systems back online with verification
Post-Incident Hardening
Strengthen defenses to prevent future attacks
- Implement stronger controls - Deploy advanced security measures
- Enforce MFA & access policies - Strengthen authentication and authorization
- Upgrade monitoring systems - Enhance detection and alerting capabilities
- Prevent future attacks - Implement lessons learned from incident
How We Secure Your Network
Our proven methodology ensures comprehensive network protection from day one
Detect
Identify breach scope and affected systems
- Alert triage and validation
- Initial impact assessment
- Stakeholder notification
Contain
Stop the attack immediately
- Isolate compromised systems
- Block malicious traffic
- Prevent lateral movement
Investigate
Trace attacker activity
- Forensic data collection
- Timeline reconstruction
- Root cause analysis
Eliminate
Remove threats completely
- Malware removal
- Backdoor elimination
- Vulnerability patching
Recover
Restore systems safely
- System validation
- Service restoration
- Monitoring activation
Harden
Prevent future incidents
- Security improvements
- Policy updates
- Team training
Why Choose DefendX in a Crisis
When every second counts, you need experts who can act decisively and effectively

Rapid Response SLA
Immediate deployment when every second matters. Our
IR team mobilizes within 15 minutes of your call,
24/7/365. No waiting for business hours. No delays.
- <15 min initial response | <2 hrs containment

Evidence Preservation
Forensic-ready reporting for audits, insurance claims,
and legal proceedings. Chain of custody maintained.
Evidence admissible in court if needed.
- Legal-grade forensics | Insurance-ready documentation

Calm & Clear Communication
We guide your leadership team step-by-step through the
crisis. No jargon. Clear action items. Regular updates.
Executive-level briefings for stakeholders.
- Dedicated IR coordinator | Executive communication

Safe Recovery
No reinfection, no corrupted backups. We verify system
integrity before restoration. Test for persistence
mechanisms. Ensure clean recovery every time.
- 100% threat elimination verified before restoration
Block Attacks Before They Reach You
Every day your systems face relentless attacks — DefendX stops them at the edge
Without expert response:
Data leaks continue
Attackers maintain access for weeks or months, exfiltrating sensitive data continuously
Systems remain compromised
Hidden backdoors and persistence mechanisms allow attackers to return at will
Recovery becomes expensive
Extended downtime, data loss, regulatory fines, and reputation damage multiply costs exponentially
With DefendX:
Attackers are removed quickly
Complete threat elimination within hours, not weeks. No persistence mechanisms left behind
Data loss is minimized
Rapid containment limits exposure window. Forensics identify exactly what was compromised
Business operations are restored fast
Structured recovery process brings systems back online safely with minimal downtime
We stop the bleeding — and rebuild stronger
Expert incident response doesn't just resolve the current crisis. We implement hardening measures to ensure the same attack vector can never be used again.
Built for Real-World Incidents
Our incident response services meet the highest standards for forensics, compliance, and legal requirements

Litigation-ready forensic reports
Chain of custody maintained. Evidence
collection follows legal standards.
Reports admissible in court proceedings.

Support for cyber insurance claims
Documentation formatted for insurance
requirements. Direct coordination with
your insurance provider. Claim
optimization support.

Compliance with ISO, SOC 2, GDPR frameworks
Response procedures aligned with regulatory requirements. Breach notification assistance. Compliance documentation support.
Frequently Asked Questions
Critical information for incident response decisions
What should I do immediately after a breach?
1) Contact our 24/7 emergency hotline immediately. 2) Do NOT shut down systems without guidance – this can destroy evidence. 3) Document what you’ve observed. 4) Isolate affected systems from the network if possible. 5) Do NOT attempt to remove malware yourself. Our team will guide you through proper containment steps that preserve forensic evidence.
Should I shut down systems?
Usually NO. Shutting down systems can alert attackers, trigger data destruction mechanisms, or lose volatile evidence in RAM. There are specific scenarios where shutdown is appropriate, but this decision should be made with IR expert guidance. Call us first – we’ll assess your specific situation and provide immediate guidance on containment actions.
How fast can you respond?
Our IR team mobilizes within 15 minutes of your call, 24/7/365. Initial containment actions typically begin within 2 hours. We have on-call specialists ready to deploy immediately, with no waiting for business hours or approval chains. For critical breaches, we can have boots on the ground at your location within hours if needed.
Will our insurance cover this?
Most cyber insurance policies cover incident response services. We work directly with insurance providers and can coordinate with your policy. Our documentation is formatted for insurance claims, and we’ve successfully supported hundreds of claims. Contact us immediately – even if you’re unsure about coverage, rapid response minimizes damage and reduces overall claim costs.
Do you work remotely or on-site?
Both. Most incident response work can be performed remotely for faster response times. However, we deploy on-site teams when needed for complex forensics, evidence collection, or situations requiring physical access. We assess your specific incident and recommend the most effective approach, often using a hybrid model.
Facing a Security Incident Right Now?
Every minute counts. Our incident response team is ready to help you contain the
breach and minimize damage.
Request Security Consultation
What You'll Get
Free Compliance Gap Assessment
Detailed analysis of your current state vs. certification requirements
Customized Roadmap
Step-by-step plan with timeline and resource requirements
Expert Consultation
30-minute call with a GRC expert to discuss your specific needs
Cost Estimate
Transparent pricing for complete certification journey