Securing Patient Data — ISO 27701 & HIPAA Alignment for a MedTech SaaS Company
ecuring proprietary engineering software & achieving certification in 4 months.
Introduction
Healthcare and medical-device software companies must protect highly sensitive patient information. A MedTech organization approached DefendX after entering the Middle East market, where privacy expectations are strict.
1. Data Protection Challenges
Handling PHI/PII
No privacy impact assessments
Weak access controls
Hospitals demanding compliance
2. Our Privacy-Focused Approach
ISO 27701 PIMS implementation
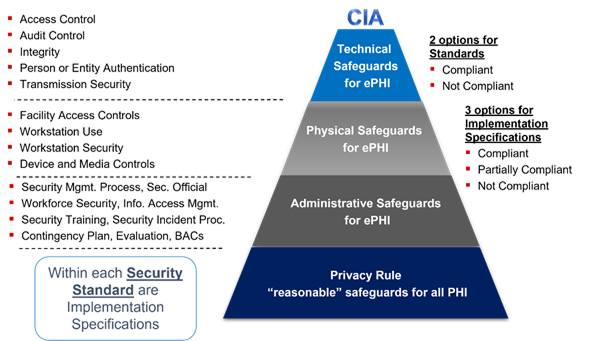
HIPAA-aligned controls
Data flow maps & risk analysis
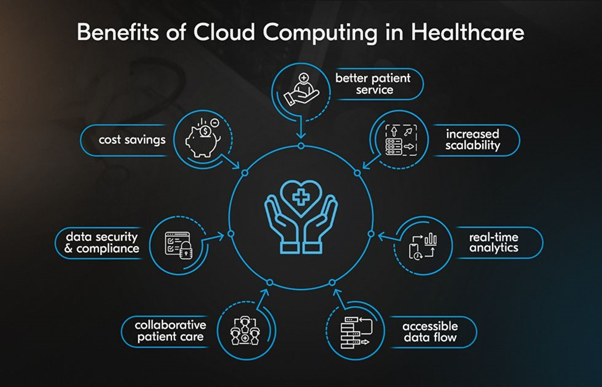
Cloud hardening
3. Final Results
Strong PHI protection
Reduced privacy risk exposure
Faster onboarding by hospital clients
Aligned with international healthcare data norms
Conclusion
Privacy-led cybersecurity is becoming a mandatory requirement for MedTech companies expanding globally.