Strengthening SaaS Security — How a Cloud CRM Startup Became ISO-Ready

ecuring proprietary engineering software & achieving
certification in 4 months.

Introduction

SaaS startups operate fast — but cyber risks move even faster. When a young cloud CRM company in Ahmedabad began onboarding enterprise clients, they faced a tough reality:

without ISO 27001 and DevSecOps maturity, growth was at risk. 

That’s where DefendX stepped in. 
1. The Challenge

The startup had: 

  • OWASP vulnerabilities 
  • Weak cloud configuration
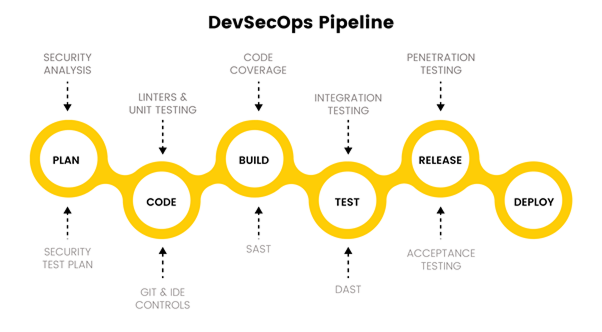
  • No structured DevSecOps 
  • Enterprise clients demanding ISO 27001

2. Our Strategy

We introduced: 

  • End-to-end VAPT
  • Cloud security fix recommendations 
  • Developer secure-coding training 
  • SAST/DAST integration 
  • ISO 27001 readiness framework 

3. Key Outcomes

  • ISO 27701 PIMS implementation 
  • HIPAA-aligned controls 
  • Data flow maps & risk analysis 
  • Cloud hardening 
  • VAPT + API penetration testing 

Final Results

  • 70% vulnerability reduction
  • Consistent secure deployments 
  • Faster enterprise onboarding 
  • ISO 27001 audit-ready maturity

Conclusion

Security is not a cost for SaaS startups — it’s a competitive advantage..